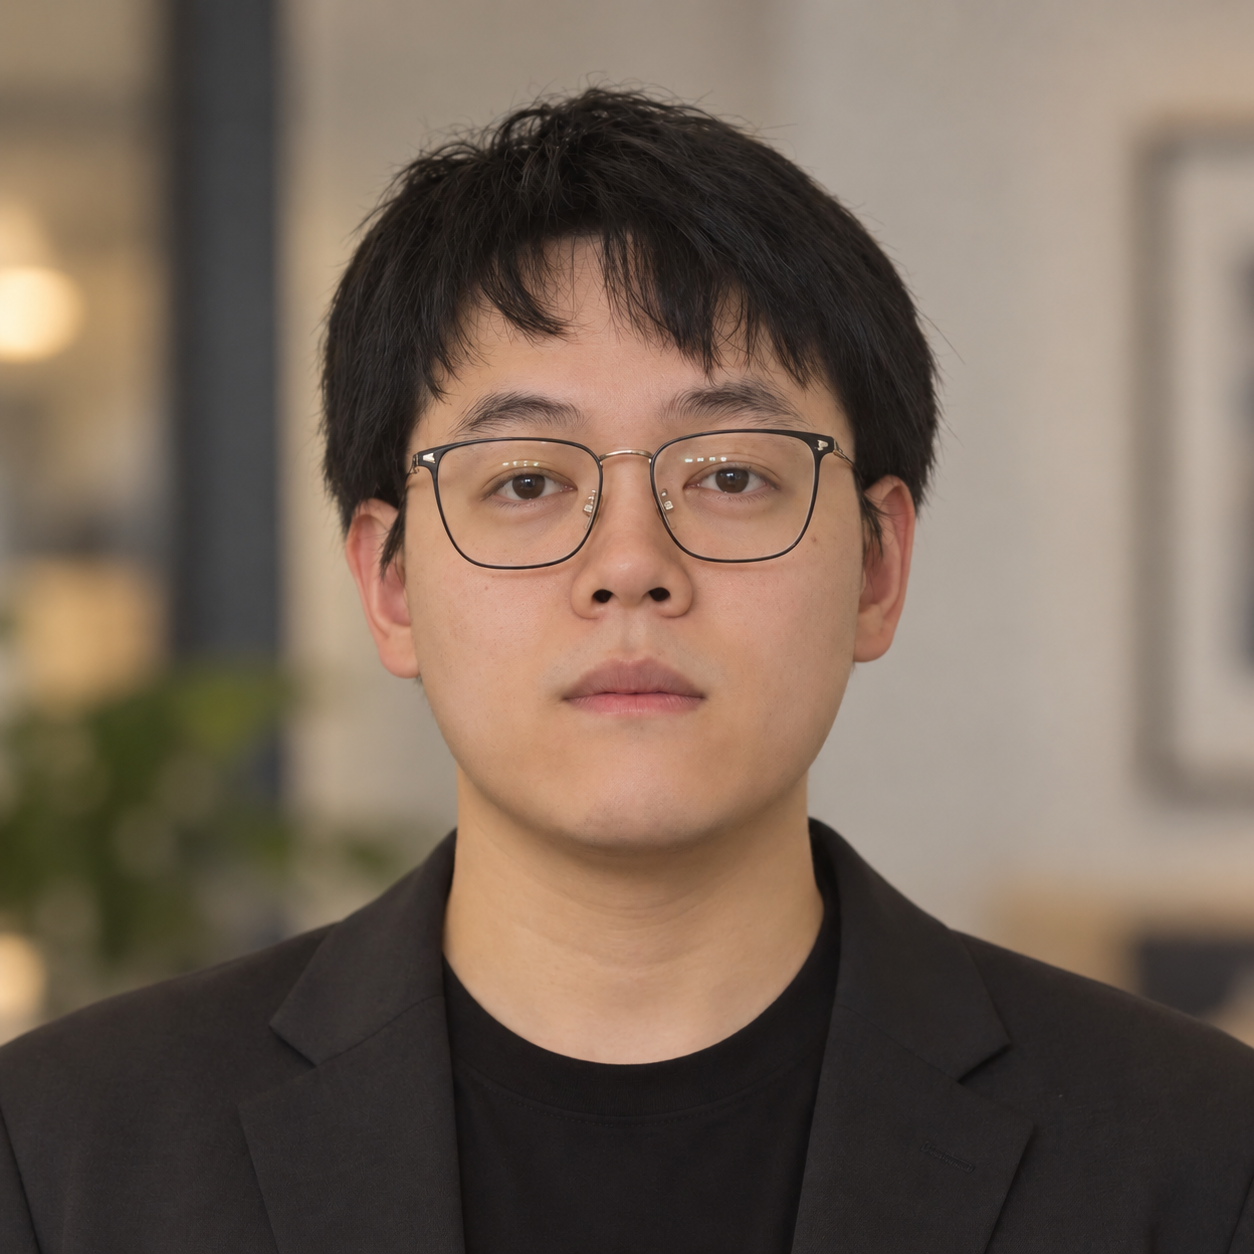
Mengyuan (Marvin) Li
Assistant Professor, University of Southern California
Thomas Lord Department of Computer Science
Ming Hsieh Department of Electrical and Computer Engineering
Recruiting PhD students for Fall 2027. USC MS and undergraduate students are also welcome. Join SEPT Lab
I lead SEPT Lab (Security, Privacy, and Trust) at USC. My research builds trustworthy computing environments by integrating hardware security mechanisms with software systems, so that data and computation stay protected on platforms from personal devices to cloud AI systems.
- Research areas
- Verifiable AI systems · Trusted execution environments (TEEs) · Confidential computing · System and hardware security · AI agent security
- Lab
 SEPT Lab ·
 verifiable.pro · SEPT Lab on GitHub
- Profiles
- Google Scholar · DBLP · USC Viterbi profile
- mengyuanli@usc.edu
About
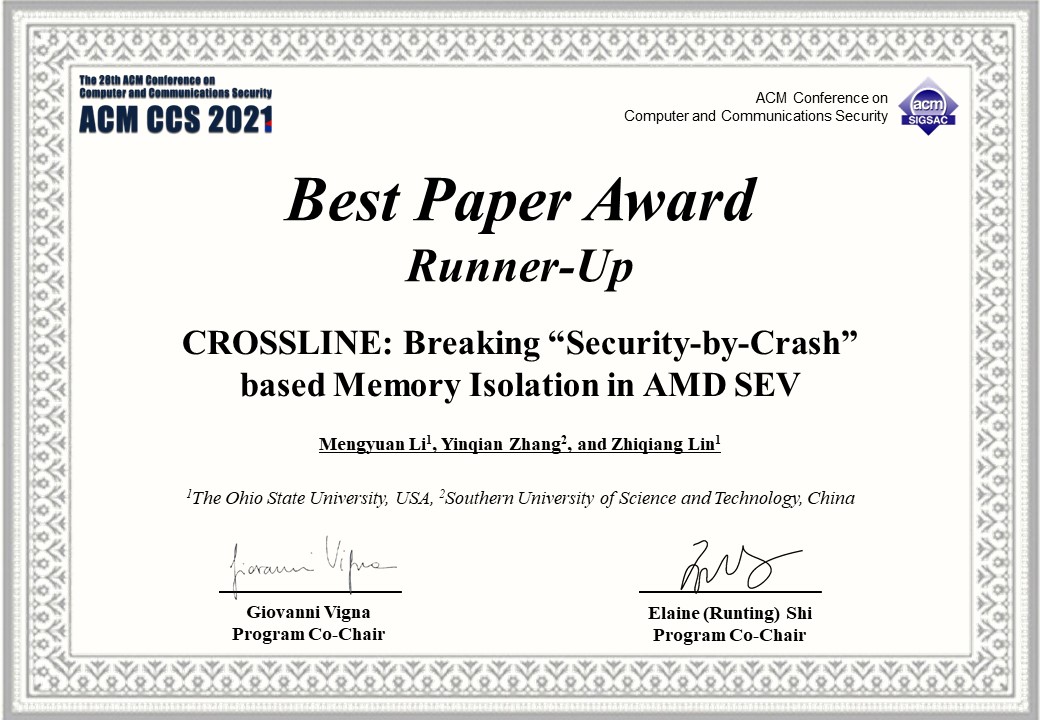
Mengyuan (Marvin) Li is an Assistant Professor in the Thomas Lord Department of Computer Science at the University of Southern California, where he leads SEPT Lab (Security, Privacy, and Trust). Before joining USC in 2024, he was a postdoctoral researcher at MIT CSAIL (2022–2024), working with Prof. Mengjia Yan. He received his Ph.D. in Computer Science and Engineering from The Ohio State University in 2022, advised by Prof. Yinqian Zhang. His research on AMD SEV led to several AMD security bulletins and CVEs, and his paper CROSSLINE received the Best Paper Award Runner-Up at ACM CCS 2021.
Research
My group pursues two research thrusts:
- Uncovering, understanding, and defending against system and hardware vulnerabilities in cloud systems, CPUs, GPUs, and AI systems.
- Co-designing software and hardware for secure and efficient AI systems.
Verifiable AI
Evidence that an AI result came from the claimed model and computation, produced without revealing sensitive data. SEPT Lab also maintains verifiable.pro, a public resource with news, explainers, and guides on verifiable AI.
Topics: zero-knowledge verification · LLM inference · model oversight
TEE and Confidential Computing
Practical hardware-isolated execution: efficient and secure TEE-based systems for cloud and AI workloads, from oblivious memory inside VM-based TEEs to confidential multi-GPU machine learning.
Topics: AMD SEV-SNP · Intel SGX · confidential VMs and GPUs · ORAM
System and Hardware Vulnerabilities
Design flaws and side channels that break the security guarantees of systems and hardware, found and disclosed to vendors such as AMD.
Topics: side channels · SEV-SNP · macOS sandboxing · GPUs
AI Agent Security
Observing and protecting agent execution with TEEs and runtime monitoring, so that agents can be trusted with sensitive data on shared infrastructure.
Topics: runtime monitoring · tool isolation · agent memory
Join SEPT Lab
Recruiting for Fall 2027
PhD students
For Fall 2027, Yue Zhao, Ruolin Li, and I are recruiting up to six PhD students together through a research cluster that spans our departments. Ruolin Li works on autonomous systems and Yue Zhao on trustworthy AI, while my group focuses on systems and security. Our shared goal is intelligent systems that remain reliable and secure when they are deployed in the real world. Students in the cluster can work with more than one of us and pursue questions that cross our research areas. Co-advising is possible but not required.
To apply, submit your application through USC Viterbi Graduate Admission (PhD application information). If you are interested in working with me, email mengyuanli@usc.edu with “[SEPT PhD]” in the subject line.
Research collaboration
Current USC MS and undergraduate students are welcome to work on research projects in SEPT Lab, and students at other universities can apply to collaborate with us. If you are interested, email mengyuanli@usc.edu with “[SEPT Research]” in the subject line.
News
Recruiting up to six PhD students for Fall 2027 in a cross-department cluster with Yue Zhao and Ruolin Li. Join SEPT Lab
MC-ORAM appears at ISCA 2026.
Hollow-LLM Attack appears at IEEE S&P 2026.
Talk at the University of Chicago: Confidential Computing and Trusted Execution Environments: Challenges and Opportunities for Trustworthy AI. (event page)
SCALE presented at HPCA 2026.
Writing in Symbiosis appears in the NeurIPS 2025 Creative AI Track.
RMP entry caching study at HASP 2025; AMD published security bulletin AMD-SB-3036.
Chekhov’s Gun appears at ACM CCS 2025.
Few-shot graph OOD detection with LLMs appears at ECML PKDD 2025.
Earlier news, 2021–2024
SoK on TEE design choices and pitfalls appears at ACM ASIACCS 2024.
Joined USC as an Assistant Professor in the Thomas Lord Department of Computer Science and started SEPT Lab.
CipherH accepted to USENIX Security 2023.
Two papers at IEEE S&P 2022: A Systematic Look at Ciphertext Side Channels on AMD SEV-SNP and vSGX.
CROSSLINE accepted to ACM CCS 2021 and received the Best Paper Award Runner-Up.
CIPHERLEAKS accepted to USENIX Security 2021; AMD issued a security bulletin and CVE.
Publications
2026 · 2025 · 2024 · Before 2024 · Preprints
Names in bold are my PhD students or students who work closely with me. * Equal contribution. Also listed on Google Scholar.
2026
- IEEE S&P Hollow-LLM Attack: Computationally Trivial Weights in Zero-Knowledge Verification of LLM Inference Chen Gong, Beijie Liu, Mengyuan Li 2026 IEEE Symposium on Security and Privacy (S&P 2026) DOI · PDF · arXiv · BibTeX
- ASPLOS WAVE: Leveraging Architecture Observation for Privacy-Preserving Model Oversight Haoxuan Xu*, Chen Gong*, Beijie Liu*, Haizhong Zheng, Beidi Chen, Mengyuan Li 31st ACM International Conference on Architectural Support for Programming Languages and Operating Systems (ASPLOS 2026) DOI · Code · BibTeX
- SeQureDB Workshop Query Cost Model Calibration in Confidential Virtual Machines Qihan Zhang, Mengyuan Li, Ibrahim Sabek Workshop on Secure and Private Data Management (SeQureDB 2026) PDF · arXiv · BibTeX
- ISCA MC-ORAM: A Mask-Assisted and Counter-Based Non-Deterministic ORAM Inside VM-Based TEEs Yongqin Wang, Rachit Rajat, Jonghyun Lee, Mengyuan Li, Murali Annavaram 53rd ACM/IEEE Annual International Symposium on Computer Architecture (ISCA 2026) DOI · BibTeX
- HPCA SCALE: Tackling Communication Bottlenecks in Confidential Distributed Machine Learning Joongun Park, Yongqin Wang, Huan Xu, Hanjiang Wu, Mengyuan Li, Tushar Krishna 2026 IEEE International Symposium on High-Performance Computer Architecture (HPCA 2026) DOI · BibTeX
2025
- ACM CCS Chekhov’s Gun: Uncovering Hidden Risks in macOS Application-Sandboxed PID-Domain Services Minghao Lin, Jiaxun Zhu, Tingting Yin, Zechao Cai, Guanxing Wen, Yanan Guo, Mengyuan Li 2025 ACM SIGSAC Conference on Computer and Communications Security (CCS 2025) DOI · BibTeX
- NeurIPS Writing in Symbiosis: Mapping Human Creative Agency in the AI Era Vivan Doshi, Mengyuan Li Advances in Neural Information Processing Systems 38 (NeurIPS 2025), Creative AI Track Paper · PDF · arXiv · BibTeX
- HASP Workshop A Close Look at RMP Entry Caching and Its Security Implications in SEV-SNP Alexis Bagia, Vincent Quentin Ulitzsch, Daniël Trujillo, Mengyuan Li, Mengjia Yan, Jean-Pierre Seifert 14th International Workshop on Hardware and Architectural Support for Security and Privacy (HASP 2025) Disclosures: AMD-SB-3036 DOI · BibTeX
- ECML PKDD Few-Shot Graph Out-of-Distribution Detection with LLMs Haoyan Xu*, Zhengtao Yao*, Yushun Dong, Ziyi Wang, Ryan A. Rossi, Mengyuan Li, Yue Zhao European Conference on Machine Learning and Principles and Practice of Knowledge Discovery in Databases (ECML PKDD 2025) DOI · PDF · arXiv · BibTeX
- TMLR Journal LEGO-Learn: Label-Efficient Graph Open-Set Learning Haoyan Xu, Kay Liu, Zhengtao Yao, Philip S. Yu, Mengyuan Li, Kaize Ding, Yue Zhao Transactions on Machine Learning Research (TMLR) Paper · PDF · arXiv · Code · BibTeX
2024
- ACM ASIACCS SoK: Understanding Design Choices and Pitfalls of Trusted Execution Environments Mengyuan Li, Yuheng Yang, Guoxing Chen, Mengjia Yan, Yinqian Zhang 19th ACM Asia Conference on Computer and Communications Security (ASIA CCS 2024) DOI · PDF · BibTeX
Before 2024
- USENIX Security 2023 CipherH: Automated Detection of Ciphertext Side-channel Vulnerabilities in Cryptographic Implementations Sen Deng, Mengyuan Li, Yining Tang, Shuai Wang, Shoumeng Yan, Yinqian Zhang 32nd USENIX Security Symposium (USENIX Security 2023) Paper · PDF · Code · BibTeX
- DIMVA 2023 PWRLEAK: Exploiting Power Reporting Interface for Side-Channel Attacks on AMD SEV Wubing Wang, Mengyuan Li, Yinqian Zhang, Zhiqiang Lin 20th Conference on Detection of Intrusions and Malware & Vulnerability Assessment (DIMVA 2023) Disclosures: AMD-SB-3004 · CVE-2023-20575 DOI · PDF · BibTeX
- IEEE S&P 2022 A Systematic Look at Ciphertext Side Channels on AMD SEV-SNP Mengyuan Li*, Luca Wilke*, Jan Wichelmann, Thomas Eisenbarth, Radu Teodorescu, Yinqian Zhang 2022 IEEE Symposium on Security and Privacy (S&P 2022) · Acceptance rate 14.0% (57/407) Disclosures: AMD-SB-1033 · CVE-2021-46744 AMD published an official white paper for TEE developers and users on writing code that resists ciphertext side channels. AMD white paper DOI · PDF · BibTeX
- IEEE S&P 2022 vSGX: Virtualizing SGX Enclaves on AMD SEV Shixuan Zhao, Mengyuan Li, Yinqian Zhang, Zhiqiang Lin 2022 IEEE Symposium on Security and Privacy (S&P 2022) · Acceptance rate 16.5% (54/327) DOI · PDF · Code · BibTeX
- PhD Thesis 2022 Understanding and Exploiting Design Flaws of AMD Secure Encrypted Virtualization Mengyuan Li Ph.D. Dissertation, The Ohio State University, 2022 Paper · BibTeX
- ACSAC 2021 TLB Poisoning Attacks on AMD Secure Encrypted Virtualization Mengyuan Li, Yinqian Zhang, Huibo Wang, Kang Li, Yueqiang Cheng 37th Annual Computer Security Applications Conference (ACSAC 2021) · Acceptance rate 17.2% (56/326) Disclosures: AMD-SB-1023 · CVE-2021-26340 · Lenovo LEN-75179 DOI · PDF · BibTeX
- ACM CCS 2021 CROSSLINE: Breaking “Security-by-Crash” based Memory Isolation in AMD SEV Mengyuan Li, Yinqian Zhang, Zhiqiang Lin 2021 ACM SIGSAC Conference on Computer and Communications Security (CCS 2021) · Acceptance rate 22.3% (196/879) Best Paper Award Runner-Up, one of 14 papers among 879 submissions that received a Best Paper Award or Runner-Up (plaque, CCS 2021 awards) DOI · PDF · arXiv · BibTeX
- USENIX Security 2021 CIPHERLEAKS: Breaking Constant-time Cryptography on AMD SEV via the Ciphertext Side Channel Mengyuan Li, Yinqian Zhang, Huibo Wang, Kang Li, Yueqiang Cheng 30th USENIX Security Symposium (USENIX Security 2021) · Acceptance rate 18.8% (248/1319) Disclosures: AMD-SB-1013 · CVE-2020-12966 AMD filed an embargo for the ciphertext side channel identified in the paper and announced a security bulletin together with a hardware patch for SEV-SNP in August 2021. Paper · PDF · Website · BibTeX
- IEEE DSC 2019 Defeating Speculative-Execution Attacks on SGX with HyperRace Guoxing Chen, Mengyuan Li, Fengwei Zhang, Yinqian Zhang 2019 IEEE Conference on Dependable and Secure Computing (DSC 2019) DOI · PDF · BibTeX
- USENIX Security 2019 Exploiting Unprotected I/O Operations in AMD’s Secure Encrypted Virtualization Mengyuan Li, Yinqian Zhang, Zhiqiang Lin, Yan Solihin 28th USENIX Security Symposium (USENIX Security 2019) · Acceptance rate 16.2% (113/697) Paper · PDF · BibTeX
- USENIX ATC 2018 Peeking Behind the Curtains of Serverless Platforms Liang Wang, Mengyuan Li, Yinqian Zhang, Thomas Ristenpart, Michael Swift 2018 USENIX Annual Technical Conference (USENIX ATC 2018) · Acceptance rate 20.1% (76/378) Paper · PDF · Code · BibTeX
- ACM CCS 2017 Stacco: Differentially Analyzing Side-Channel Traces for Detecting SSL/TLS Vulnerabilities in Secure Enclaves Yuan Xiao, Mengyuan Li, Sanchuan Chen, Yinqian Zhang 2017 ACM SIGSAC Conference on Computer and Communications Security (CCS 2017) · Acceptance rate 17.9% (151/843) DOI · PDF · arXiv · Code · BibTeX
- IEEE IoT-J 2017 Journal SPFM: Scalable and Privacy-Preserving Friend Matching in Mobile Cloud Mengyuan Li, Na Ruan, Qiyang Qian, Haojin Zhu, Xiaohui Liang, Le Yu IEEE Internet of Things Journal, vol. 4, no. 2, 2017 DOI · BibTeX
- ACM CCS 2016 When CSI Meets Public WiFi: Inferring Your Mobile Phone Password via WiFi Signals Mengyuan Li, Yan Meng, Junyi Liu, Haojin Zhu, Xiaohui Liang, Yao Liu, Na Ruan 2016 ACM SIGSAC Conference on Computer and Communications Security (CCS 2016) · Acceptance rate 16.5% (137/831) DOI · PDF · Slides · Demo video · Video · BibTeX
- IEEE JSAC 2016 Journal You Can Jam But You Cannot Hide: Defending Against Jamming Attacks for Geo-Location Database Driven Spectrum Sharing Haojin Zhu, Chenliaohui Fang, Yao Liu, Cailian Chen, Mengyuan Li, Xuemin Sherman Shen IEEE Journal on Selected Areas in Communications, vol. 34, no. 10, 2016 DOI · BibTeX
Preprints
- 2026 Safety Offset Learning: When Benign Fine-Tuning Misaligns LLMs Jesson Wang*, Zhanhao Hu*, Minghao Lin, Yuchen Wu, Aylin Caliskan, Mengyuan Li arXiv:2610.25611, 2026 PDF · arXiv · Code · BibTeX
- 2026 CatchBench: When Can an Agent Failure Be Caught? Yue Zhao, Mengyuan Li, Ruolin Li, Prince Zizhuang Wang, Shuli Jiang, Linsey Pang, Xiongye Xiao, Xiyang Hu arXiv:2608.22808, 2026 PDF · arXiv · Code · BibTeX
- 2026 Hiding Directions, Leaking Structure: Breaking ArrowCloak through Low-Rank Structure Beijie Liu*, Junyi Ouyang*, Haoxuan Xu*, Vincent Quentin Ulitzsch, Potung Yu, Yajie Zhao, Mengyuan Li arXiv:2608.21615, 2026 PDF · arXiv · BibTeX
- 2026 Behavioral Skill Reconstruction: Reconstructing Hidden Functionality from LLM Agent Skills Peichun Hua, Haoxuan Xu, Mengyuan Li arXiv:2608.04192, 2026 PDF · arXiv · BibTeX
- 2026 OTRO: Oblivious Tokenization Path with Square-Root ORAM Jonghyun Lee, Yongqin Wang, Rachit Rajat, Daniel Wong, Mengyuan Li, Murali Annavaram arXiv:2606.17358, 2026 PDF · arXiv · BibTeX
- 2026 Infrastructure for Valuable, Tradable, and Verifiable Agent Memory Mengyuan Li, Lei Gao, Haoxuan Xu, Jiate Li, Potung Yu, Lingke Cheng, Yue Zhao, Murali Annavaram arXiv:2603.24564, 2026 PDF · arXiv · Code · BibTeX
- 2025 A Systematic Study of Model Extraction Attacks on Graph Foundation Models Haoyan Xu*, Ruizhi Qian*, Jiate Li, Yushun Dong, Minghao Lin, Hanson Yan, Zhengtao Yao, Qinghua Liu, Junhao Dong, Ruopeng Huang, Yue Zhao, Mengyuan Li arXiv:2511.11912, 2025 PDF · arXiv · BibTeX
- 2025 VReaves: Eavesdropping on Virtual Reality App Identity and Activity via Electromagnetic Side Channels Wei Sun, Minghong Fang, Mengyuan Li arXiv:2506.17570, 2025 PDF · arXiv · BibTeX
- 2025 GLIP-OOD: Zero-Shot Graph OOD Detection with Graph Foundation Model Haoyan Xu*, Zhengtao Yao*, Xuzhi Zhang, Ziyi Wang, Langzhou He, Yushun Dong, Philip S. Yu, Mengyuan Li, Yue Zhao arXiv:2504.21186, 2025 PDF · arXiv · BibTeX
- 2025 Graph Synthetic Out-of-Distribution Exposure with Large Language Models Haoyan Xu*, Zhengtao Yao*, Ziyi Wang, Zhan Cheng, Xiyang Hu, Mengyuan Li, Yue Zhao arXiv:2504.21198, 2025 PDF · arXiv · BibTeX
- 2024 Ditto: Elastic Confidential VMs with Secure and Dynamic CPU Scaling Shixuan Zhao*, Mengyuan Li*, Mengjia Yan, Zhiqiang Lin arXiv:2409.15542, 2024 PDF · arXiv · BibTeX
- 2024 Bridge the Future: High-Performance Networks in Confidential VMs without Trusted I/O devices Mengyuan Li, Shashvat Srivastava, Mengjia Yan arXiv:2403.03360, 2024 PDF · arXiv · BibTeX
Teaching
- Spring 2027 (upcoming)
CSCI 530: Security Systems
Graduate course on protecting computer networks and systems with cryptography, authentication and authorization, and intrusion detection and response. A lab component gives students hands-on experience with these mechanisms.
- Fall 2025, Fall 2026
CSCI 699: Understanding and Identifying Side-Channel Threats in Cloud and LLM Systems
Graduate seminar on side-channel attacks across multi-tenant cloud platforms, TEEs, GPUs, and LLM services.
- Spring 2025, Spring 2026
CSCI 699: Confidential Computing: Protecting Your Data on Cloud GPUs and CPUs
Graduate course on trusted execution environments, confidential VMs, and confidential GPUs, together with related privacy techniques such as federated learning, secure multi-party computation, and fully homomorphic encryption.
Service
Program committee
ACM Conference on Computer and Communications Security (CCS) 2024; IEEE European Symposium on Security and Privacy (EuroS&P) 2024; International Conference on Applied Cryptography and Network Security (ACNS) 2023.
Journal reviewer
IEEE Transactions on Dependable and Secure Computing (TDSC) 2021, 2022, 2023; IEEE Transactions on Parallel and Distributed Systems (TPDS) 2023; IEEE Transactions on Mobile Computing (TMC) 2021, 2022; IEEE/ACM Transactions on Networking (TNET) 2021, 2022; IEEE Transactions on Emerging Topics in Computing 2022.
External reviewer
IEEE Symposium on Security and Privacy (Oakland) 2020, 2022, 2023; ACM CCS 2019, 2020, 2022, 2023; USENIX Security Symposium 2021; ISOC Network and Distributed System Security Symposium (NDSS) 2019; ACM AsiaCCS 2020; ACM Cloud Computing Security Workshop (CCSW) 2021.
Contact
Ginsburg Hall (GCS), 1031 Downey Way
Los Angeles, CA 90089